Fintech at the White House

by Cherian Abraham 5 min read June 15, 2016

FintechWhiteHouse

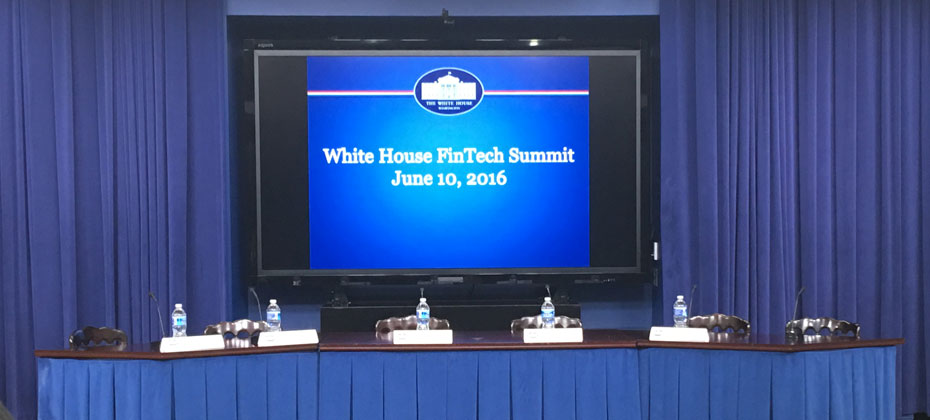
Last Friday, I attended a private session on FinTech at the White House – alongside a few others in the financial services ecosystem – Founders, Investors, Academics, a handful of Financial institutions and Regulators. Titled “The White House FinTech Summit” – the intent was to promote a discussion, sans media, on what could be done better to progress innovation in financial services, as well as communicate the administration’s own perspective on topics such as Financial inclusion, Regulatory arbitrage, Cyber Security, and Big Data.

I am only writing down what resonated most, with me – so this isn’t meant to be a complete account of the half day event.

Startups and Regulation: The need for a radically simpler engagement model
I wasn’t surprised that this view was articulated half an hour into the summit – by Bruce Wallace of SVB, on a panel hosted by Secretary Penny Pritzker of the US Department of Commerce. Asked what the Govt role in fostering an environment for innovation, should be: Bruce summarized it best (and I am paraphrasing): “A FinTech startup has only a limited amount of time and scope to focus on the myriad state and federal agencies and regulators on understanding and interpreting policy. We need a radically simpler and transparent engagement model.”

On this topic of “what should we be doing more to encourage startups to come to US” I would have liked Stripe to chime in here, with what they are likely to have learned from launching Atlas – I call it “Company in a Box” – which is a suite of services including banking and payment processing to enable entrepreneurs to maintain a presence in the US and sell to the US consumer.

Regulatory Sandbox to Test, Proves and if need be – Fail
Unsurprisingly, the incumbents echoed much of the same view, and Adam Carson of Chase suggested that “the regulatory climate is making it hard for FIs to experiment, collaborate – and where applicable, fail quickly. And thus, we should be advocating for a sandbox of sorts – that allows institutions to not have to be burdened so much by regulation as they attempt to test and learn – before worrying about scale and burdensome regulation”. Adam is absolutely right in that consumers no longer compare their banking experience on Chase’s platform to that of Capital One or Citi or BofA – they compare those digital experiences to that on Facebook, Amazon, Google, Apple, and Uber. I have written before on the same topic (see below):

“As banking moves from branch to app – from a wholly owned and curated experience inside a branch – TO – an app that vies for space in a “democratized” and crowded home screen, banks must realize that they no longer own the entire canvas. Instead they merely follow the design principles set by the most-used apps on our phones. I no longer compare my bank app with that of another bank, I compare it against the services I use often – Facebook, Twitter, Gmail, Apple Pay, Uber etc. And if who you compete with on this platform has been redrawn to include brands who have nothing to do with managing money – then you have to try as hard not to be boxed in as a bank.

Having both the talent required to design these new experiences, and the capital to acquire them will only serve to further differentiate banks that have this focus as a priority vs those who will in the end get wrapped.”

Risk of Algorithmic bias as FinTech ingests alternative data
Representatives from a couple of agencies – were a bit more cautionary in their approach to the topic of FinTech, scaling distribution and the focus around Big data, with Urban affairs asking FinTech firms to be cognizant of algorithmic bias in their models – because the data that drives decisions could be slanted or skewed towards a particular demographic – and used civil rights as an example.

Playing fast and loose with consumer data
Anjan Mukherjee of Treasury focused on Cybersecurity – and Chris Carroll (from John Hopkins) warned of a potential “Asteroid impact” manifesting in a data breach involving one or more FinTech firms – which could cause an inexorable exodus of trust away from the upstarts towards the incumbents. I understand the sentiment, and we have had a couple of examples where a couple of the startups have invited criticism around data handling and security – and this topic invites further scrutiny in light of EU PSD2 as well as the banking incumbents clamping down on access to customer account data.

There is much agreement that screen scraping and sharing customer credentials with personal finance apps and aggregators is inadvisable – but to not consider that these rather poor approaches emerged only in the absence of a genuine, bank approved framework or API, would be a missed opportunity to understand why these exist in the first place. We do need secure methods for consumers to transfer customer data to 3rd party platforms or aggregators to extract more value out of the interactions with their bank. And we need guidelines to make it easy and transparent – so that consumers can make an informed decision after having considered the apparent cost and benefits involved.

I hope we will sort this out soon – between Banks, Startups, Consumer Advocates and Regulators – not just because a systems breach is inevitable that will sweep up millions of unsafely stored consumer banking credentials – but the opportunity to create standards, improve security and create a level playing field for all will be the only desirable outcome to discussions such as the one on last Friday.

Much thanks to Adrienne Harris at the White House, for hosting this event and inviting us to join this debate.
Related Posts

New data indicate signs of increased VantageScore 4.0 adoption. Recent Experian Capital Markets data reporting points to gradual growth in VantageScore 4.0 adoption, and more loans beginning to appear in a larger share of GSE pools.

November 20, 2026 by Angad Paintal
What Is a Ransomware Attack? How to Prepare and Respond

Ransomware attacks can create challenges that extend far beyond an organization’s IT systems. When critical applications become unavailable or sensitive information is compromised, businesses may face operational disruption, financial losses and difficult decisions about how to support affected customers. While cybersecurity defenses are essential, organizations also need clear response procedures, coordinated communication and recovery plans. Understanding how ransomware attacks happen, their potential impact and the steps organizations can take to prepare can help businesses respond more effectively when an incident occurs. What is a ransomware attack? A ransomware attack is a type of cyberattack in which criminals use malicious software or extortion tactics to demand payment from an organization. Traditionally, ransomware encrypts files or systems, preventing authorized users from accessing information until a ransom is paid. Some attackers also steal sensitive data and threaten to release it unless their demands are met. These tactics may occur separately or together, creating challenges for organizations trying to restore operations and protect sensitive information. Paying a ransom does not guarantee that attackers will restore access, delete stolen information or refrain from making additional demands. How do ransomware attacks happen? Ransomware attacks often begin when cybercriminals gain unauthorized access to an organization’s systems or accounts. Once inside, attackers may attempt to expand their access, steal information or deploy malicious software. Common attack methods include: Phishing and social engineering: Deceptive emails or messages that trick employees into opening malicious attachments, visiting harmful websites or sharing login credentials Compromised credentials: Stolen passwords or authentication information used to access business systems and accounts Unpatched vulnerabilities: Security weaknesses in software, servers or network devices that attackers exploit Third-party access: Compromised vendors or connected systems that provide a potential entry point Malicious downloads: Harmful software installed through deceptive websites, compromised applications or unsafe downloads Understanding these methods can help organizations identify potential weaknesses and strengthen their security practices. How do ransomware attacks affect businesses and customers? The consequences of a ransomware attack depend on the systems affected, the information involved and the organization's ability to contain the incident. Business disruption and financial losses When critical systems become unavailable, organizations may experience interruptions to customer service, payment processing, internal operations or other essential functions. The financial impact can be significant. According to the FBI's 2025 Internet Crime Report, reported ransomware-related losses reached approximately $32.3 million, up from $12.5 million in 2024. These figures do not capture the full financial impact of ransomware incidents, including business interruption, recovery expenses and other indirect costs. Customer data exposure and fraud risks Some ransomware incidents involve the theft of sensitive information, potentially exposing customers to identity theft or fraud. If attackers obtain login credentials or personal information, organizations may also need to consider related threats, including account takeover. Customer trust and reputation Customers expect organizations to protect their information and communicate clearly when incidents affect them. Delayed or confusing communication may create additional uncertainty. A coordinated response can help organizations provide timely information and appropriate support to affected individuals. What should organizations do after a ransomware attack? When a ransomware incident is suspected, organizations should activate their incident response procedures and work with qualified professionals to assess and contain the threat. Important response steps include: Activate the response team: Bring together IT, cybersecurity, legal, privacy, communications and leadership teams as appropriate. Contain the incident: Identify affected systems and take steps to limit further unauthorized activity while preserving relevant evidence. Investigate the impact: Determine which systems and information may have been compromised, including whether sensitive data was accessed or removed. Evaluate notification requirements: Work with legal and privacy advisers to determine applicable regulatory, contractual and customer communication obligations. Support affected customers: Prepare clear communications and appropriate resources when personal information has been exposed. An established data breach response strategy can help organizations coordinate customer notification and support activities following an incident. How can organizations prepare for and recover from ransomware attacks? Organizations can prepare for ransomware attacks by combining security controls, tested backups, employee training and a documented incident response plan. Recovery planning should also address how teams will restore systems, assess data exposure and communicate with affected customers. Key preparedness measures include: Maintain secure backups: Keep protected backups and regularly test restoration procedures. Strengthen access controls: Implement multifactor authentication and limit access to sensitive systems. Update software: Address known vulnerabilities through consistent patch management. Train employees: Help staff recognize phishing attempts and suspicious activity. Monitor security threats: Use appropriate detection and monitoring tools to identify potential attacks. Test response plans: Conduct exercises that evaluate technical recovery, communication and decision-making responsibilities. Following an incident, recovery should focus on restoring systems safely, addressing remaining vulnerabilities and evaluating potential risks to affected individuals. Organizations may also need to consider whether compromised information could contribute to additional fraud. Depending on the circumstances, fraud prevention solutions may support broader identity risk management efforts. Security teams should also evaluate related threats, including automated bot attacks, when assessing potential misuse of compromised accounts or credentials. Once operations are restored, reviewing lessons learned can help organizations strengthen their security controls, response procedures and future preparedness. How can breach response planning help protect customers? Ransomware preparedness should account for both operational recovery and the potential impact on customers. If sensitive information is compromised, organizations may need to coordinate notifications, respond to customer questions and provide appropriate support. Experian® offers data breach resolution services that help organizations plan for and manage customer-facing aspects of a breach, including notification management and response support. By establishing response procedures before an incident, organizations can improve coordination and prepare to address customer needs when a breach occurs. Prepare for a more coordinated breach response Explore Experian's data breach response solutions and learn how to plan for customer notification and support. Explore data breach response solutions Download the 2027 Data Breach Response Guide

November 20, 2026 by Julie Lee
How GenAI Fraud Bots Fly Under the Radar (and How to Ground Them Before It’s Too Late)

Today’s AI-powered fraud bots are exceptionally good at mimicking human behavior. Learn why a modern defense strategy is key.

November 18, 2026 by Laura Burrows

Subscribe to our Newsletter

Enter your name and email for the latest updates.

This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.

Subscribe to our Newsletter

Don't miss out on the latest industry trends and insights!
Subscribe
