Lifecycle of a Ransomware Attack – Learnings from NetDiligence Cyber Risk Summit

by Michael Bruemmer 5 min read July 28, 2021

Ransomware needs to be on your radar. Here’s why.

Ransomware review

Ransomware is a cyberattack where cybercriminals take over an organization’s computer network with malware. Once they assume control, the criminals demand a ransom to restore the victim’s encrypted data access. With an estimated generation of $412 million in 2020 alone1, the frequency of these attacks is growing.

At Experian, we handle many data breach cases and know that7 of 10 breaches involve ransomware. This summer, NetDiligence dedicated a panel at its Cyber Risk Summit on the Lifecycle of a Ransomware Event and invited us to talk about our solutions to help business leaders prepare to minimize interruptions spurred by ransomware.

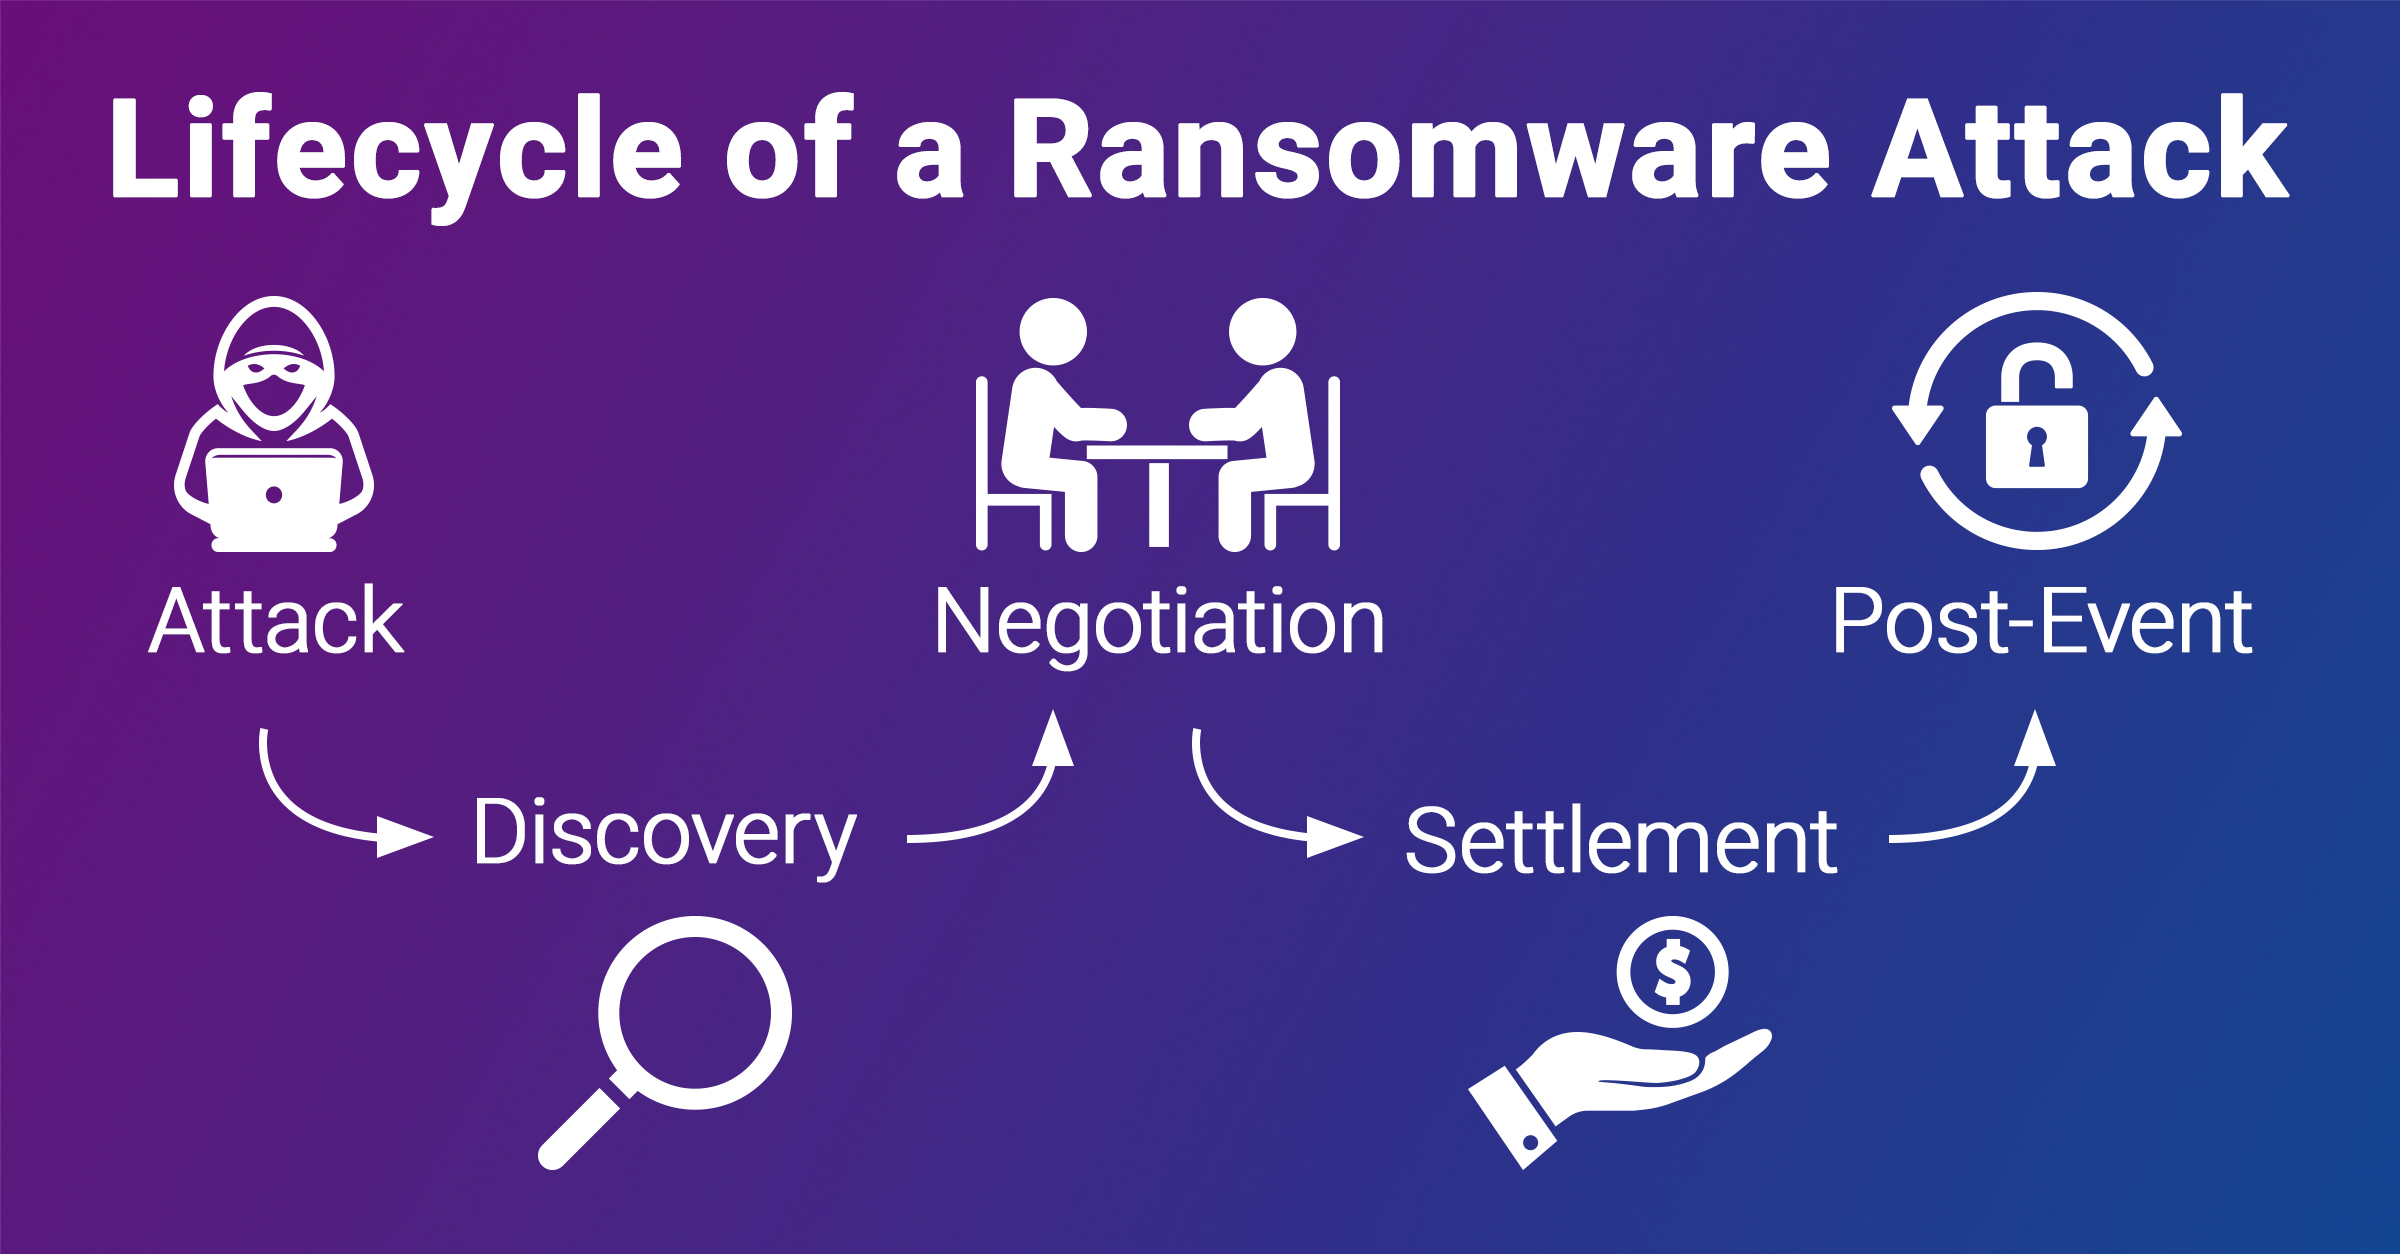
The lifecycle of a ransomware attack includes five stages:
Ransomware Attack

1. Attack

Bad actors attack to discover assets, take data, extort it for direct payment, or profit from reselling data on the dark web. They can also launch a‘double-take’ attack: first collecting ransom to access data and demanding secondary payment to keep it off the dark web. Hackers prey on company networks, searching for vulnerabilities and accessing encrypted files through phishing or planting malicious links to infect the network with malware. More than double the global rate of 14%2, U.S ransomware attacks have become more aggressive, accounting for 30% of all cyberattacks in 20202. At Experian, we’ve seen an even higher occurrence, with 59% of the events serviced 2021 to date involving ransomware.

2. Discovery

Once attackers infiltrate a system, they demand a ransom for the decryption key to unlock the encrypted files. Companies usually discover the attack through a ransom note emailed to an executive, a file left on a server, or even a flashing warning on all connected computers. If they leave a message including their contact information, ransom sum, payment delivery time, and consequences for unmet conditions, such as tipping off the media, releasing stolen data, or selling it on the dark web.

Next, companies will contact their cyber insurance carrier to log stolen information, get systems back online, navigate legal issues, and facilitate hacker negotiations. Since only about one-third of companies have cyber insurance, most will rush to hire cybersecurity counsel post-attack3, amounting to more stress and delays since it can take months for large companies or those without backups to determine the extent of the damage.

At Experian, almost allevents involving ransomware take about 20% more time to begin breach notification. Whether there is an incident plan in place or not, companies experience immense panic.

3. Negotiation

Typically, a company will hire a professional, either directly or through their cyber insurance, to negotiate with hackers. While hackers expect price haggling, the ransom price could still be hefty. According to the cybersecurity firm, Coveware, the average ransom was $154,000 in Q4 2020, down from $230,000 the year before4. But hackers can drive up the price. Prime example: JBS, the world’s largest meat processor, paid an $11 million ransom in June 2021 to prevent customer data from being compromised.

In a perfect world, the ransomware negotiation process goes this way:

  • Establish communication with the attackers
  • Obtain proof of decryption
  • Obtain data exfiltration proof
  • Negotiate a (huge) discount
  • Celebrate

Unfortunately, negotiations can be tricky, and the process rarely goes this way. Sometimes attackers go “dark” or request additional payments. Additionally, decryption tools may have bugs that skip mapped network drives or skip folders with long paths and unusual characters.

An investigation is key to determine how hackers got in, what was exposed, and if they still have access—knowing exactly how and what was compromised will help in the negotiation.

4. Settlement

After the ransom negotiations are over, companies must carefully consider the strategy behind the decision to pay or not to pay the ransom. The FBI generally discourages ransom payments because they may entice other criminals to engage in ransomware and paying does not guarantee data recovery. Additionally, the Office of Foreign Asset Control (OFAC) has payment bans and restrictions that support national security that must be upheld or face fines. At this stage, companies need to ensure that the ransom settlement does not violate constantly evolving regulations.

If companies settle, the payment will typically be delivered via cryptocurrency like Bitcoin since it is harder to detect the payees. The hackers will mix the bitcoin for others diluting the currency flow and making it difficult to trace.

5. Post-Event

For many companies, the settlement is just the beginning of ransomware attack costs. Companies will also have to pay to restore back-ups, rebuild systems and implement stronger cybersecurity controls to avoid future attacks. As discussed at the Cyber Risk Summit, here are five recommendations for companies to enforce tighter cyber control:

  1. Advanced Endpoint Monitoring System
  2. Restrict Remote Desktop Protocol (RDP)
  3. Regularly Update Software and Operating Systems
  4. Implement Password Management Policies
  5. Establish and Update Incident Response Plan and Ransomware Playbook

Ransomware is just getting started. To minimize the impact of an attack, companies create a proactive preparedness plan. Determining to protect and scan for threats, establish negotiation and payment rules, and external breach communications, is critical.

Breaches are our business at Experian. We know ransomware breaches have more complex FAQs, letter versions, and increased call center escalations.

To learn howExperian’s Reserved Responsesolution can prepare your business for a data breach,click here.

Sources:

1Washington Post, “How Ransomware Attacks Work”, July 2021

2Verizon 2021 Data Breach Investigations Report

3Washington Post, “Ransomware Axa Insurance Attacks”, June 2021

4Covewave, “Ransomware Marketplace Report”, Q4 2020

Related Posts

Building for Bots in the AI Age: Separating Legitimate Agents From Fraudsters

See how NeuroID helps businesses distinguish legitimate AI agents from fraud bots, while Agent Trust verifies agent-initiated transactions.

October 29, 2026 by Laura Burrows
2026 Retail Banking Identity and Fraud Report 

Learn how banks can convert rising fraud investment into protection customers recognize, value and feel in our recent report. Read more!

October 28, 2026 by Laura Burrows
One Platform, Fewer Handoffs, Faster Decisions

The average credit union manages between 100-300 vendor relationships, and nearly a third have no dedicated staff managing them. What was supposed to drive efficiency is stunting growth and compromising the member experience. Application volume is continuing to rise, and consumers expect a loan decision at digital speed. But for credit unions, meeting that expectation isn't the only goal. They must also continue to make the right lending decisions while also prioritizing risk management. The institutions pulling ahead aren't the ones with the most tools. They're the ones that have turned credit, fraud and decisioning into a single, coordinated system. A single loan decision touches: Credit data Identity verification Fraud signals Decisioning logic Reporting Rarely does all of that live in one place. More often, it’s stitched together across separate platforms, each with its own contract and its own support line. When a credit view and a fraud view are generated separately, they must be reconciled instead of read together in the same instant. Every handoff is a place where a decision slows down and a signal gets missed. It's why a fraud pattern that would be obvious next to the credit file often surfaces only after the funds are already gone. Fragmentation also makes it harder to optimize lending strategies over time. When data, analytics and decisioning are disconnected, credit unions have less visibility into what's working, what's changing and where strategies need to be adjusted. An integrated decisioning ecosystem closes those seams by design, with credit, fraud and lending strategy running on one platform and accessed through a single Application Programming Interface (API). Identity and compliance capabilities can be an integrated decisioning flow. The data doesn't need to be reconciled after the fact because it was never separated in the first place. Stop overengineering, start removing friction When decisioning underperforms, the instinct is to build something more custom: a proprietary model, tighter segmentation, more configuration.  Custom modeling has its place for institutions with the scale and data to justify it. But often, for small or mid-sized credit unions, the bigger opportunity is a flexible decisioning strategy that uses a strong, continuously refreshed model. This shouldn't be either/or. The right approach gives credit unions a strong decisioning strategy today, with the ability to introduce more customized analytics and modeling as their needs evolve.  The same principle applies to strategy management: credit unions can gain greater control through self-service capabilities as they build a more sophisticated data science team.   That kind of flexibility is important as credit unions modernize their decisioning infrastructure. Research surveying more than 2,000 senior credit risk and fraud decision-makers across 11 countries found that organizations investing in unified platforms and modern infrastructure are moving faster and realizing the greatest Return on Investment (ROI).   As their needs evolve, credit unions can adjust decisioning strategies without introducing another layer of technology or relying on third parties to make every change. Until self-service is the right fit, choose a partner that understands what makes your credit union’s membership and risk appetite different from others.  Same member, same afternoon, faster answer Consider a credit union growing its auto and personal loan originations.  A member applies for an auto loan on Saturday afternoon. Credit data, identity and fraud signals are read together in a single real-time pass instead of separate reviews:  Most applications resolve immediately, approved or declined based on a more comprehensive view of the applicant. A smaller number are flagged for quick step-up verification and cleared within minutes. Only genuinely ambiguous cases reach an underwriter, who is working from one complete picture instead of reconciling multiple signals. The member has an answer before the weekend is over. The credit union books the loan before competitors even open on Monday. Built to scale This kind of process holds up today. However, the better test is whether it holds up eighteen months from now when application volume has grown, new products are live and the data flowing through the system looks nothing like it does right now. Future-proofing isn't only about handling more volume. It's about having room to be nimbler and make adjustments as quickly as the market changes. A credit union that relies on standard models within a decisioning strategy may want more customized analytics and greater control over its strategies tomorrow. Connect with us With more than three decades of credit expertise and one of the industry's largest data footprints, Experian helps credit unions do more than solve this year's friction. We're helping to build a decisioning foundation that scales, so growth becomes something the system absorbs, rather than something it must be rebuilt around. Explore More

October 21, 2026 by Zohreen Ismail

Subscribe to our Newsletter

Enter your name and email for the latest updates.

This site is protected by reCAPTCHA and the Google Privacy Policy and Terms of Service apply.

Subscribe to our Newsletter

Don't miss out on the latest industry trends and insights!
Subscribe

